The Quiet Risk in Pharma's AI Rush: Nobody Owns the Governance
Everyone in pharma is talking about AI adoption. Far fewer are talking about who's accountable when an AI system gets a decision wrong.
That's a problem, because the regulators have already started talking about it.
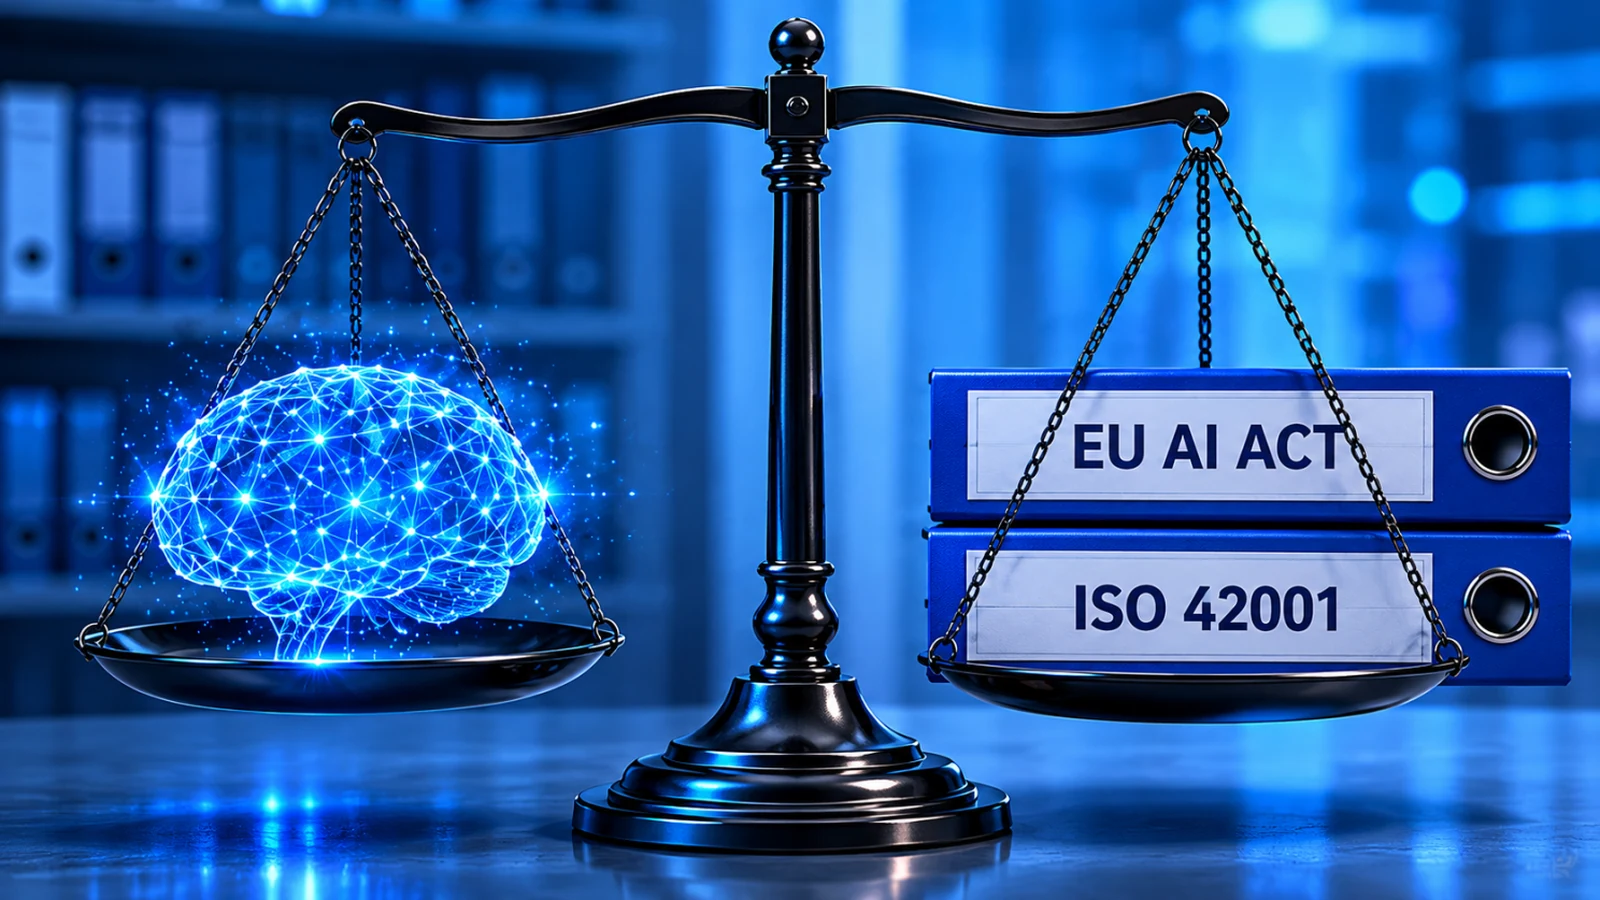
The EU AI Act is now in force, and a lot of what pharma does with AI lands squarely in its higher-risk categories, anything touching patient safety, clinical decision support, or pharmacovigilance. Meanwhile ISO 42001, the first management-system standard for AI, gives organizations a framework to actually govern these systems instead of governing them in a slide deck. Two different instruments, same underlying message: deploying AI now comes with documentation, oversight, and accountability requirements you can't bolt on later.
What keeps happening on the ground
A team stands up a model to triage adverse event reports or screen literature. It works. It saves real time. And then someone in quality asks the obvious questions: Who validated this? What data did it train on? What happens when it's wrong? How do we explain it to an inspector? And the room goes quiet.
The technology was the easy part. The governance was the part nobody assigned.
What "good" actually looks like
It's less dramatic than people fear:
Governance as the accelerator
The instinct in a regulated industry is to slow everything down until the rules are perfectly clear. But that's not the move here. The organizations getting this right are using governance as the thing that lets them move faster, because their legal, quality, and clinical teams trust the systems enough to actually approve them.
Governance isn't the brake on AI in pharma. Right now, it's looking like the accelerator.
If your team is deploying AI faster than it's governing it, that gap is worth closing before an auditor closes it for you.
What's your organization leaning on first, ISO 42001 as a framework, or building straight to EU AI Act compliance?